
Grant and audit resource access
Where: a resource's Share action, Project → Sharing, or Organization → Access. Resource owners share individual assets; organization managers inspect the administrative view permitted to their role.
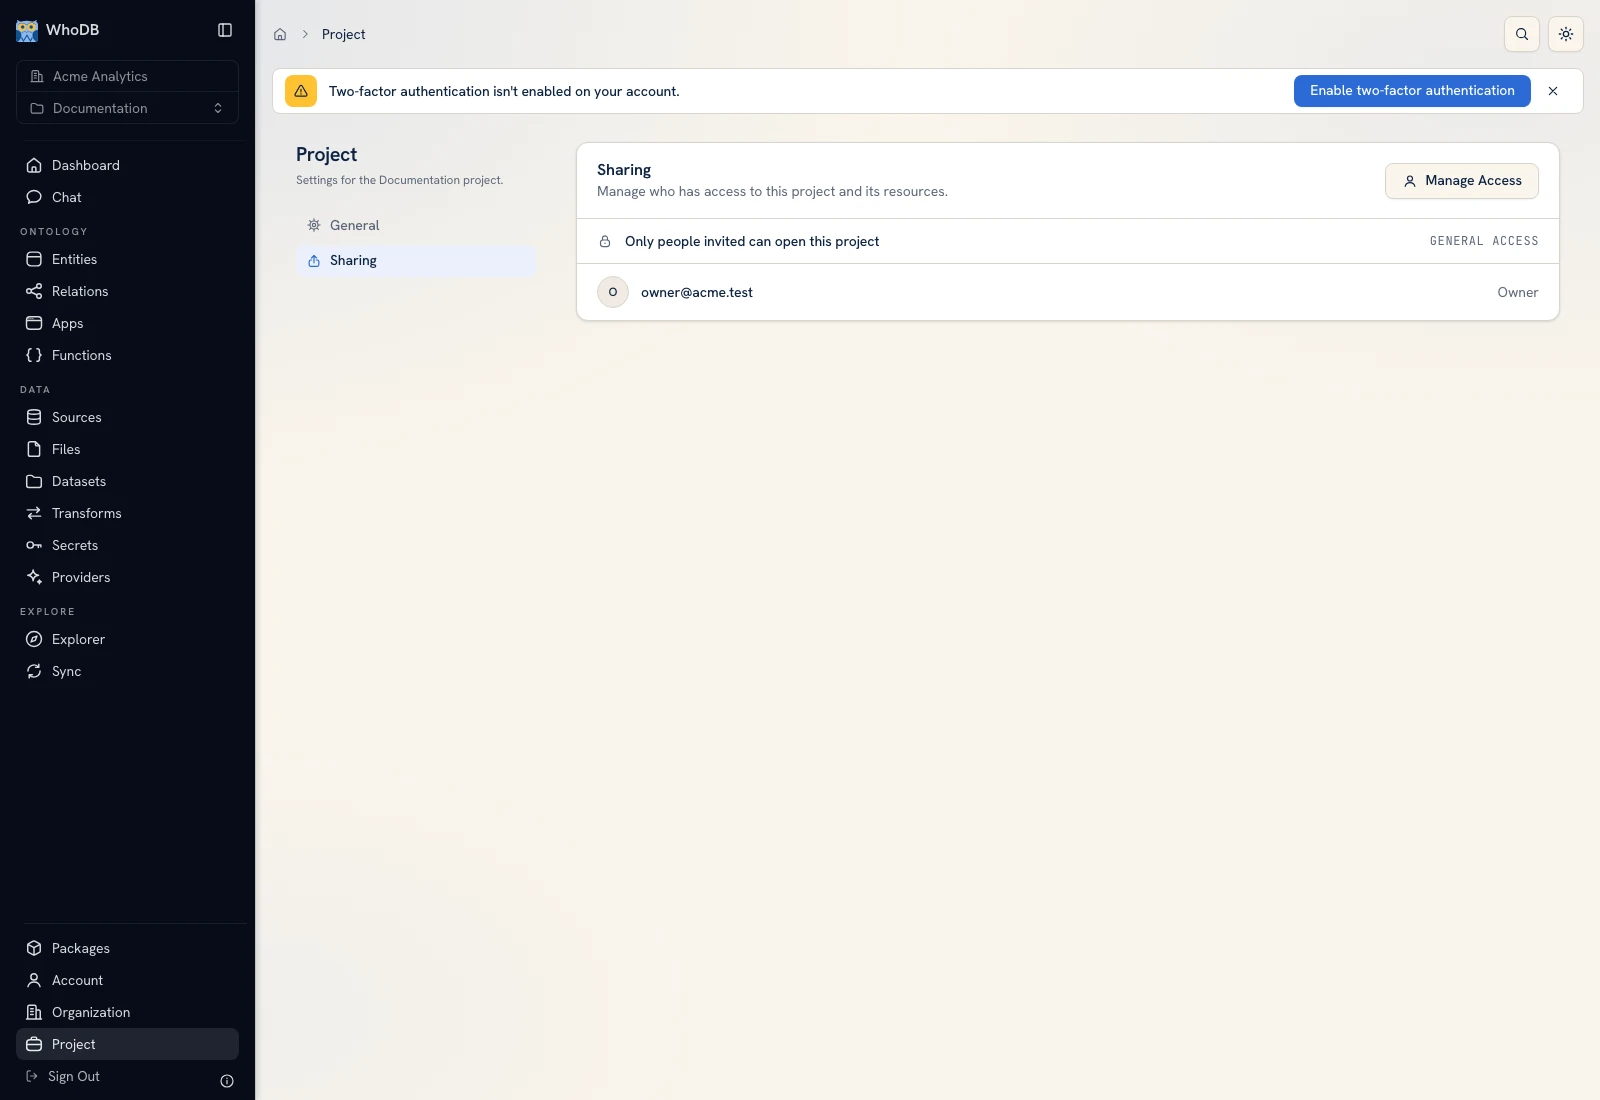 Project Sharing distinguishes general access and people with direct access.
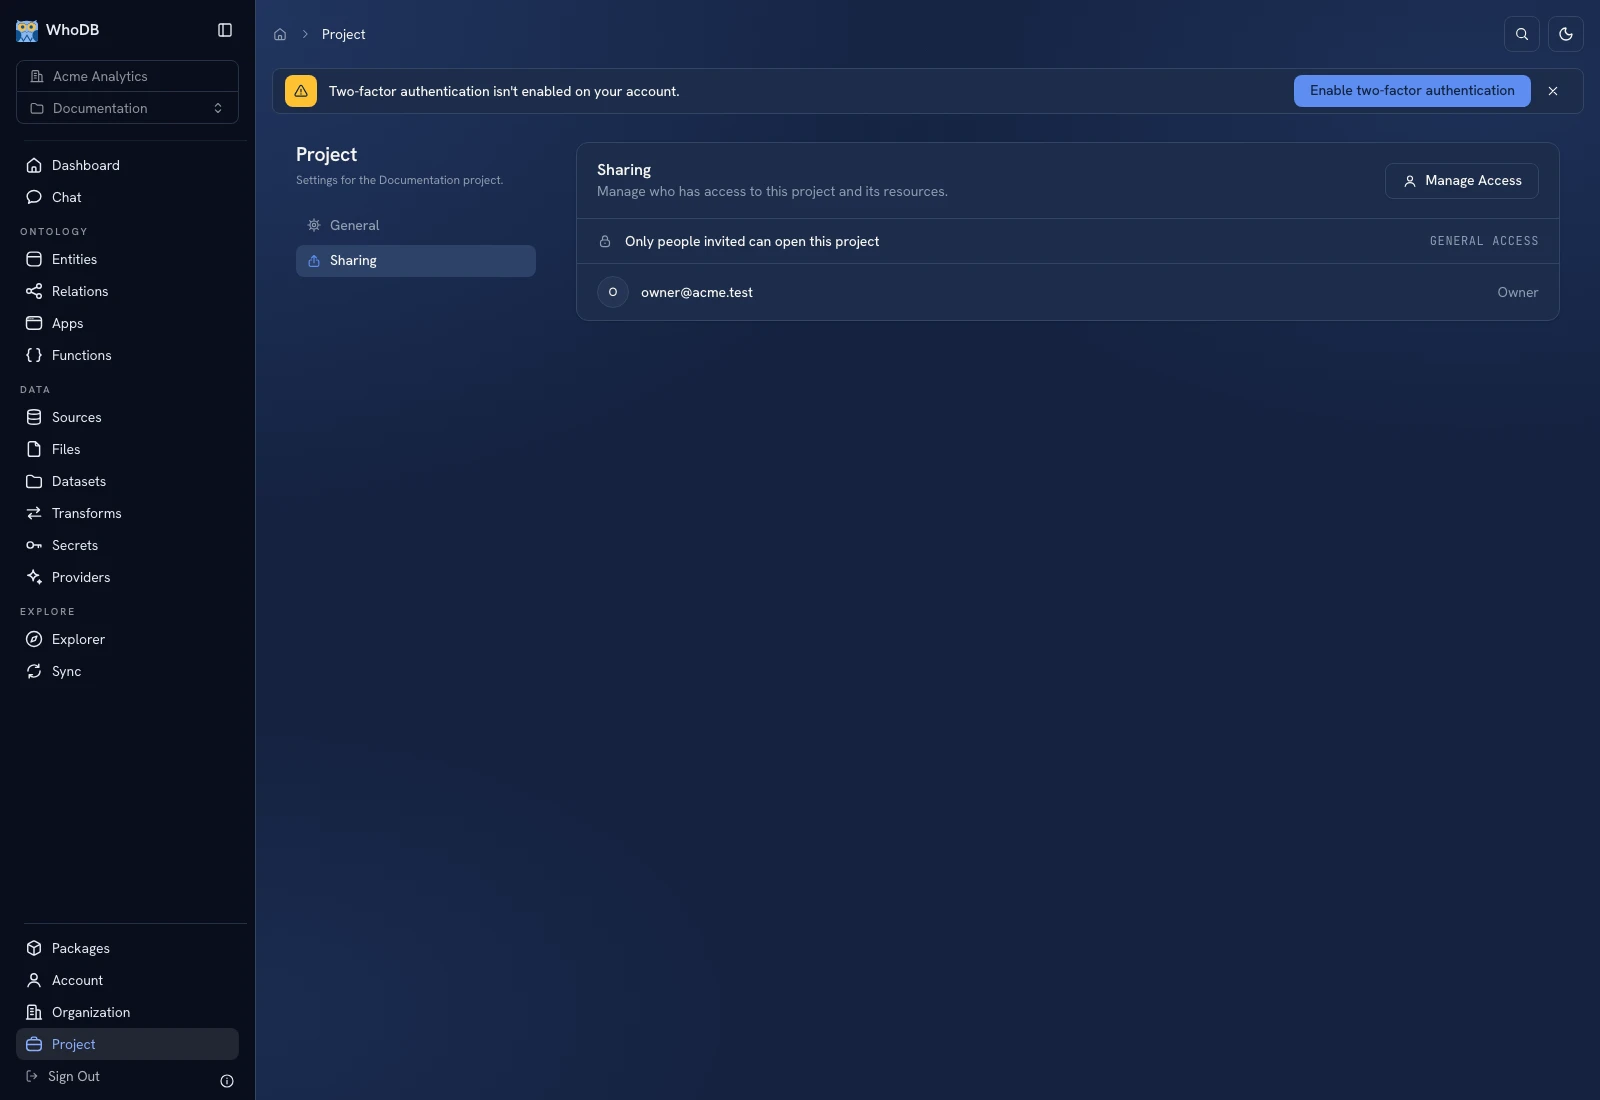 Project Sharing distinguishes general access and people with direct access.
Project general access#
Open Project → Sharing. Inspect General access: the screen distinguishes an organization-accessible project from an invite-only project. Review People with access and use Manage Access for the intended grants.
Project visibility does not erase individual-resource authorization checks. Verify the exact action on the exact resource using the recipient's account.
Resource roles#
| Role | Intended access |
|---|---|
| Owner | View, edit, run, share, delete |
| Editor | View, edit, run, export; not share or delete |
| Viewer | View; not modify, run, or share |
| Executor | Run applicable resources without edit/share access |
These are different from organization Owner/Admin/Member roles. Organization administration does not automatically expose private child-resource data.
Share an app workflow#
Open the app's Share controls and choose the person/team and role. Then inspect its bound function/entity requirements. An app invocation needs Viewer access to the app and Executor access to its bound function; nested calls require execution access to their target functions too. An Executor can run the applicable active function version without seeing its source.
Inspect grants#
Open Organization → Access and switch between By person and By resource. Locate the intended identity or resource and review its direct grants. Use this view to diagnose a denied operation or an unexpected exposure.
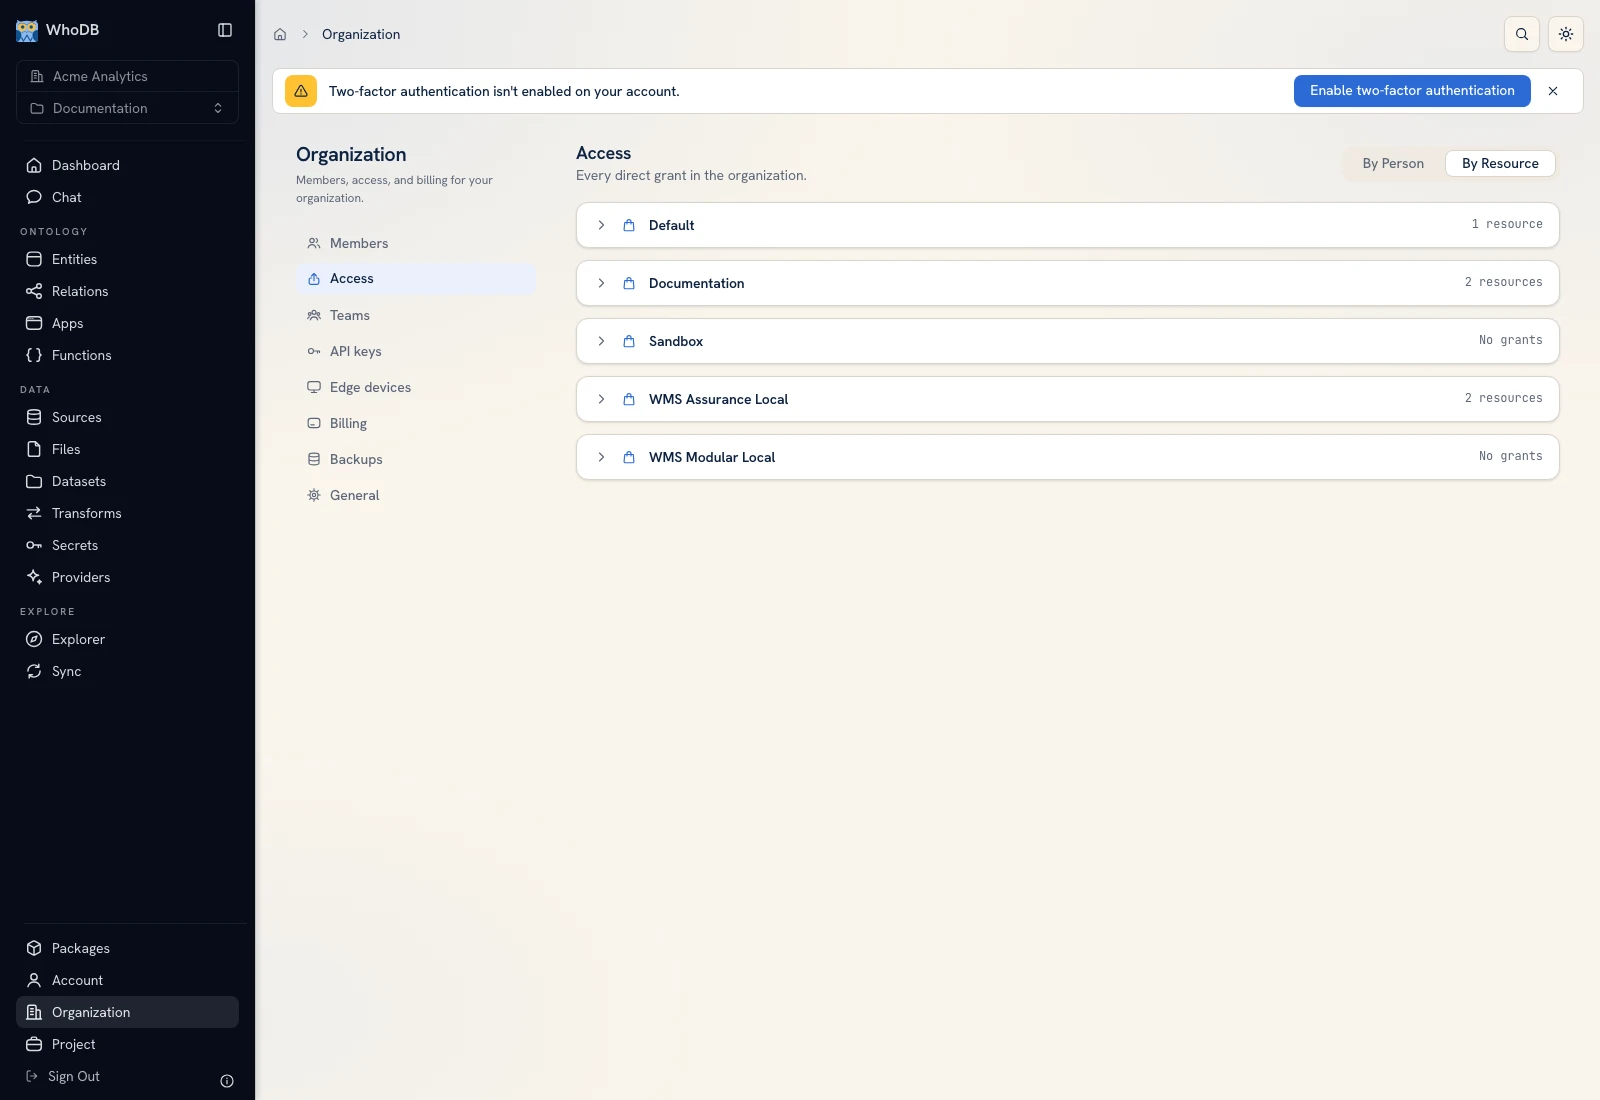 Organization Access provides person and resource views of direct grants.
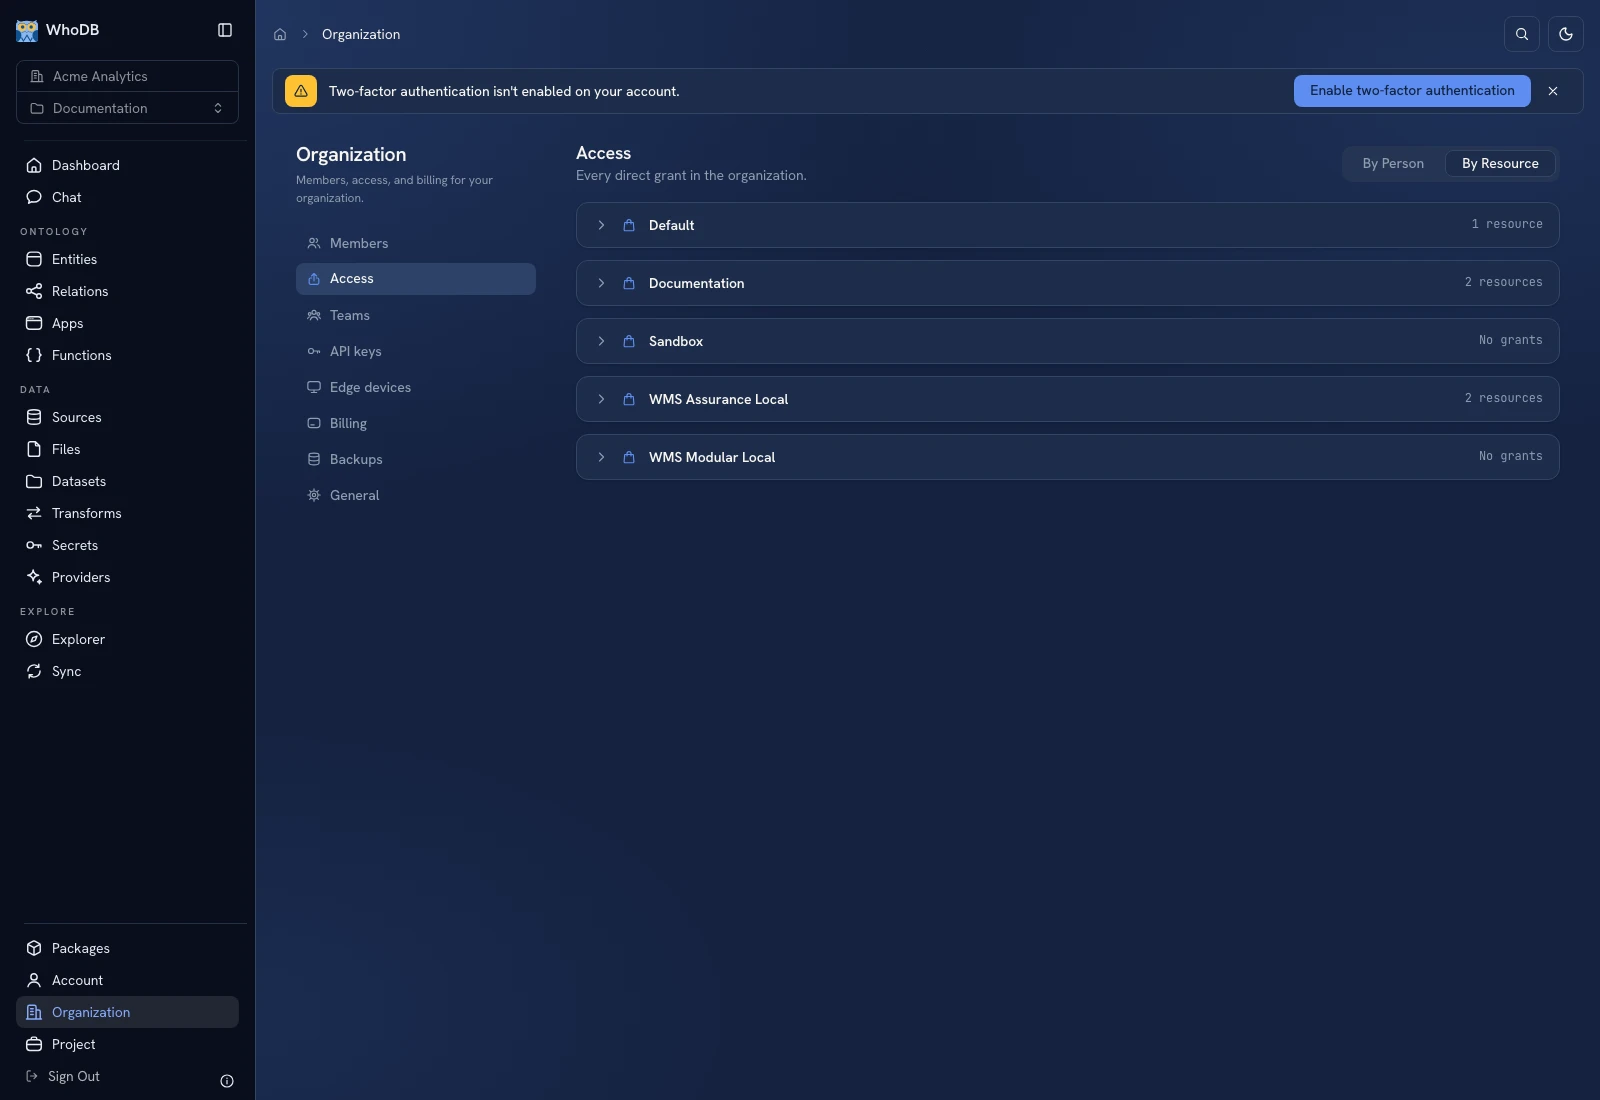 Organization Access provides person and resource views of direct grants.
Record the organization, project, caller, resource, and operation when debugging. Test again after changing a grant. Do not infer permission from the fact that the resource was visible to the person who created it.
Was this page helpful?